
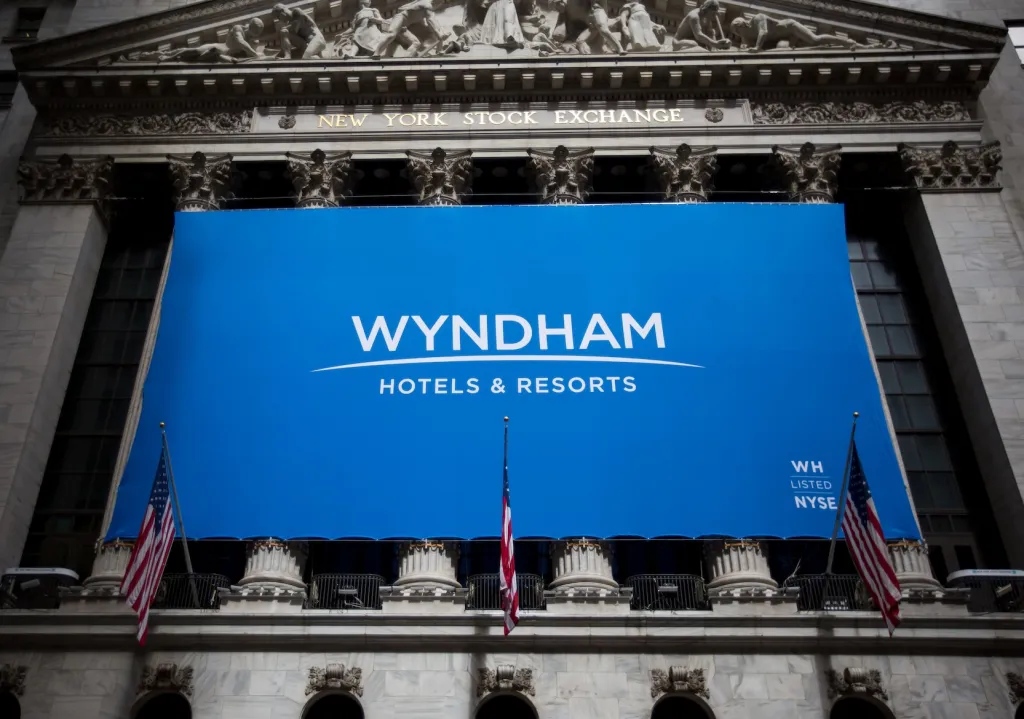
One password hidden in an app’s source code was all it took. Hotel giant Wyndham has acknowledged a cybersecurity incident after a security researcher found a hardcoded credential inside its Android app that opened the door to an internal database full of customer data. The case is a textbook example of how a single leaked secret in mobile code can expose records at the scale of a global hotel chain.
Here is what the researcher found, what data was exposed, what Wyndham has said so far, and what you should do if you hold a Wyndham Rewards account.
What Happened: The Hardcoded Password
Security researcher Robert Wiggins at What Security told TechCrunch that he found a password inside the source code of Wyndham’s Android app. The credential granted access to an internal company database hosted by Salesforce. Anyone who extracted the string from the app could reach the database without any further authentication.
- Where the flaw was found: a hardcoded credential in Wyndham’s Android app source code
- What it opened: an internal database hosted on Salesforce
- Who found it: Robert Wiggins, What Security, reported exclusively to TechCrunch
- When it was reported: published by TechCrunch on November 9, 2026
Hardcoded credentials are one of the oldest mistakes in application security, and mobile apps make them easy to find. Anyone can download an APK and decompile it. Secrets baked into client code are effectively public, which is why security guidance has said for years that app binaries must never carry live database passwords.
What Customer Data Was Exposed
According to Wiggins, the database contained personal information including customer names, email addresses, and Wyndham member numbers. It also stored customer login tokens, known as JWTs, which keep customers logged into their apps without repeatedly entering passwords. Beyond account data, the database also held Wyndham files and documents.
The JWT exposure is the most serious part of the haul. These tokens are effectively session keys. Someone holding a valid token can impersonate the logged-in user inside the app until the token expires, without ever knowing the account password. Combined with names and member numbers, the data set is a ready-made kit for targeted phishing or account takeover attempts.
Wiggins said the database had millions of entries, though he could not determine an accurate count of exposed customer records. Wyndham says it has some 129 million enrolled rewards members worldwide, so even a partial overlap would be significant. Source: TechCrunch.
How Researchers Find Flaws Like This
The method behind this find is worth understanding because it requires no exotic tooling. Mobile security researchers routinely download public APK files and decompile them into readable code. Strings that look like database connection details, API keys, or internal URLs then show up in plain sight. Wiggins found the Wyndham password by reading what the app shipped to every user’s phone.
This is also why the fix has to come from the server side. Removing the string from the next app update does not help users running older versions, and copies of the old APK will circulate for years. The durable fix is to revoke the credential entirely and re-issue access with proper authentication, which is the question security teams will be asking Wyndham next.
What Wyndham Has Said
Wyndham has acknowledged the cybersecurity incident after the good-faith disclosure. However, the company would not say whether it has the ability to check for any past unauthorized access to the database. That question matters. If the credential sat in the app for a long period, there is no public confirmation yet of who else may have found and used it before the researcher reported it.
The incident is the latest in a string of exposures in the hospitality sector, where loyalty databases hold verified names, emails, and travel patterns that are valuable to fraudsters. Our earlier coverage of hotel loyalty account theft explains why these records command a premium on underground markets.
What Wyndham Guests Should Do Now
Until Wyndham confirms the scope and timeline of the exposure, treat your Wyndham Rewards account as potentially affected. Practical steps:
- Change your Wyndham account password, and if you reused that password anywhere else, change it there too.
- Log out of all active sessions after changing the password so any captured JWT tokens lose their value.
- Review your rewards account for bookings, point transfers, or profile changes you did not make.
- Expect phishing emails that reference real booking details. Names, emails, and member numbers were exposed, so scam mails can look convincing. Never click links in booking alerts. Go to the official app or site directly.
- Watch for password reset emails you did not request. That is a common sign someone is probing your account.
- Enable any account alerts Wyndham offers for profile and reservation changes.
Lessons for App Developers
For teams shipping mobile apps, this incident is a free lesson in what not to do.
- Never hardcode secrets in client code. Use short-lived tokens issued after user authentication and keep database credentials server-side only.
- Run secret scanning in CI so credentials never reach a build artifact.
- Scope tokens to the minimum data a client needs. An app session token should not unlock an internal database.
- Audit what internal systems third-party hosting platforms like Salesforce expose to mobile clients.
- Assume the app binary is public. Anyone can decompile an APK or IPA within minutes.
The JWT detail is worth repeating in any postmortem. Session tokens in the wrong hands bypass passwords entirely, so token lifetimes, revocation paths, and device binding all deserve a second look after an incident like this.
Why Hotels Stay in the Breach Headlines
Hospitality companies keep showing up in data exposure stories because their loyalty databases are unusually rich. A hotel chain knows your full name, email, travel dates, destinations, payment patterns, and membership tier. That combination is far more useful for convincing phishing than a leaked password list from a forum.
Wyndham Hotels and Resorts operates thousands of properties worldwide and reports around 129 million enrolled rewards members. Even a small slice of that member base sitting in an unsecured database represents a large pool of verified customer identities. If you travel for work and hold multiple hotel loyalty accounts, incidents like this are a good prompt to audit which accounts share the same email and password.
FAQ
Was Wyndham hit by a data breach in 2026?
Wyndham acknowledged a cybersecurity incident after researcher Robert Wiggins found a hardcoded password in its Android app that exposed an internal customer database. The report was published by TechCrunch on November 9, 2026.
What information was exposed in the Wyndham incident?
The database contained customer names, email addresses, Wyndham member numbers, JWT login tokens, and Wyndham files and documents. The researcher described millions of entries but could not confirm an exact record count.
Is the Wyndham app safe to use now?
Wyndham has acknowledged the incident, but has not shared technical details of the fix or a timeline. Change your password, log out of all sessions, and watch for phishing until the company confirms the credential has been removed and the scope of access is known.
What is a JWT token and why does it matter here?
A JWT is a login token that keeps you signed in without re-entering your password. Because these tokens were exposed, anyone holding one could impersonate an active session, which is why resetting your password and logging out of all sessions is the recommended first step.
